


OpenCode hacked, users urged to revoke their API keys
OpenCode supports models from different AI providers, allowing developers to use the open-source coding tool with their own API keys. Now, OpenCode has emailed users warning that third-party keys saved in their workspaces may have been exposed in a breach. Several users say their provider accounts have already been charged for activity they did not authorise.
In the email, OpenCode says someone gained unauthorised access to a legacy system it was in the process of decommissioning. The company also warns that API keys stored in users’ workspaces may have been exposed, including those for OpenAI and Anthropic. These keys allow applications to use the connected AI services, so someone who obtains one could make requests at the account holder’s expense.
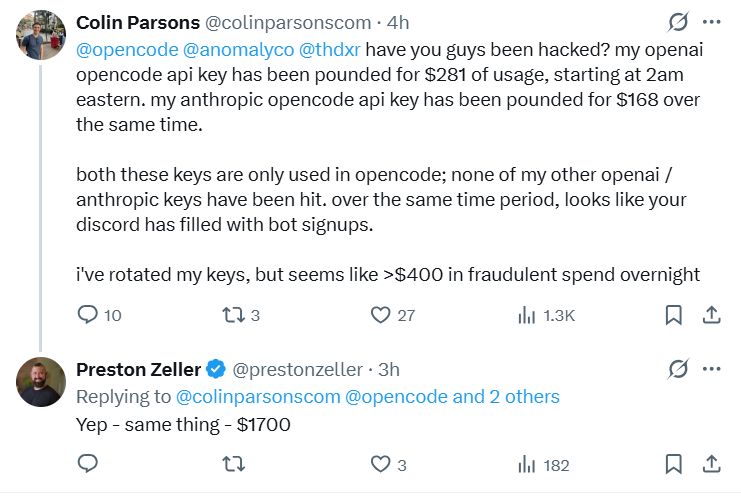
The Reddit thread contains several reports of unexpected spending. One user reported $400 in unauthorised charges on an Anthropic account, while another said Google usage charges had reached around €200 and their project had been suspended for excessive abuse. A commenter also said they received usage alerts from both OpenAI and Anthropic before OpenCode notified them of the breach.
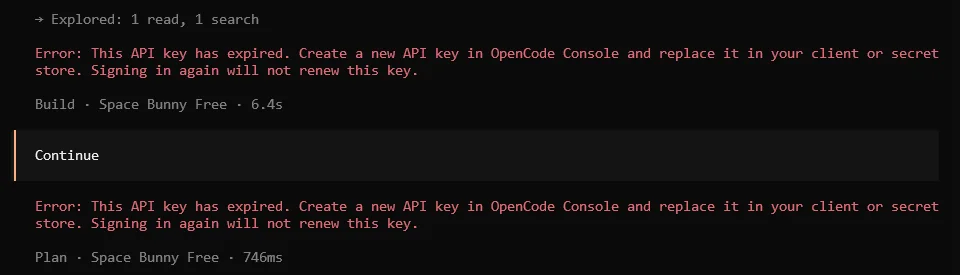
Access to OpenCode has also become a problem for some users. They say their OpenCode service API keys expired and attempts to sign in through Google or GitHub returned “Unable to start social login.” One user eventually signed in and generated a replacement key after several attempts, while another said their new key still did not work.
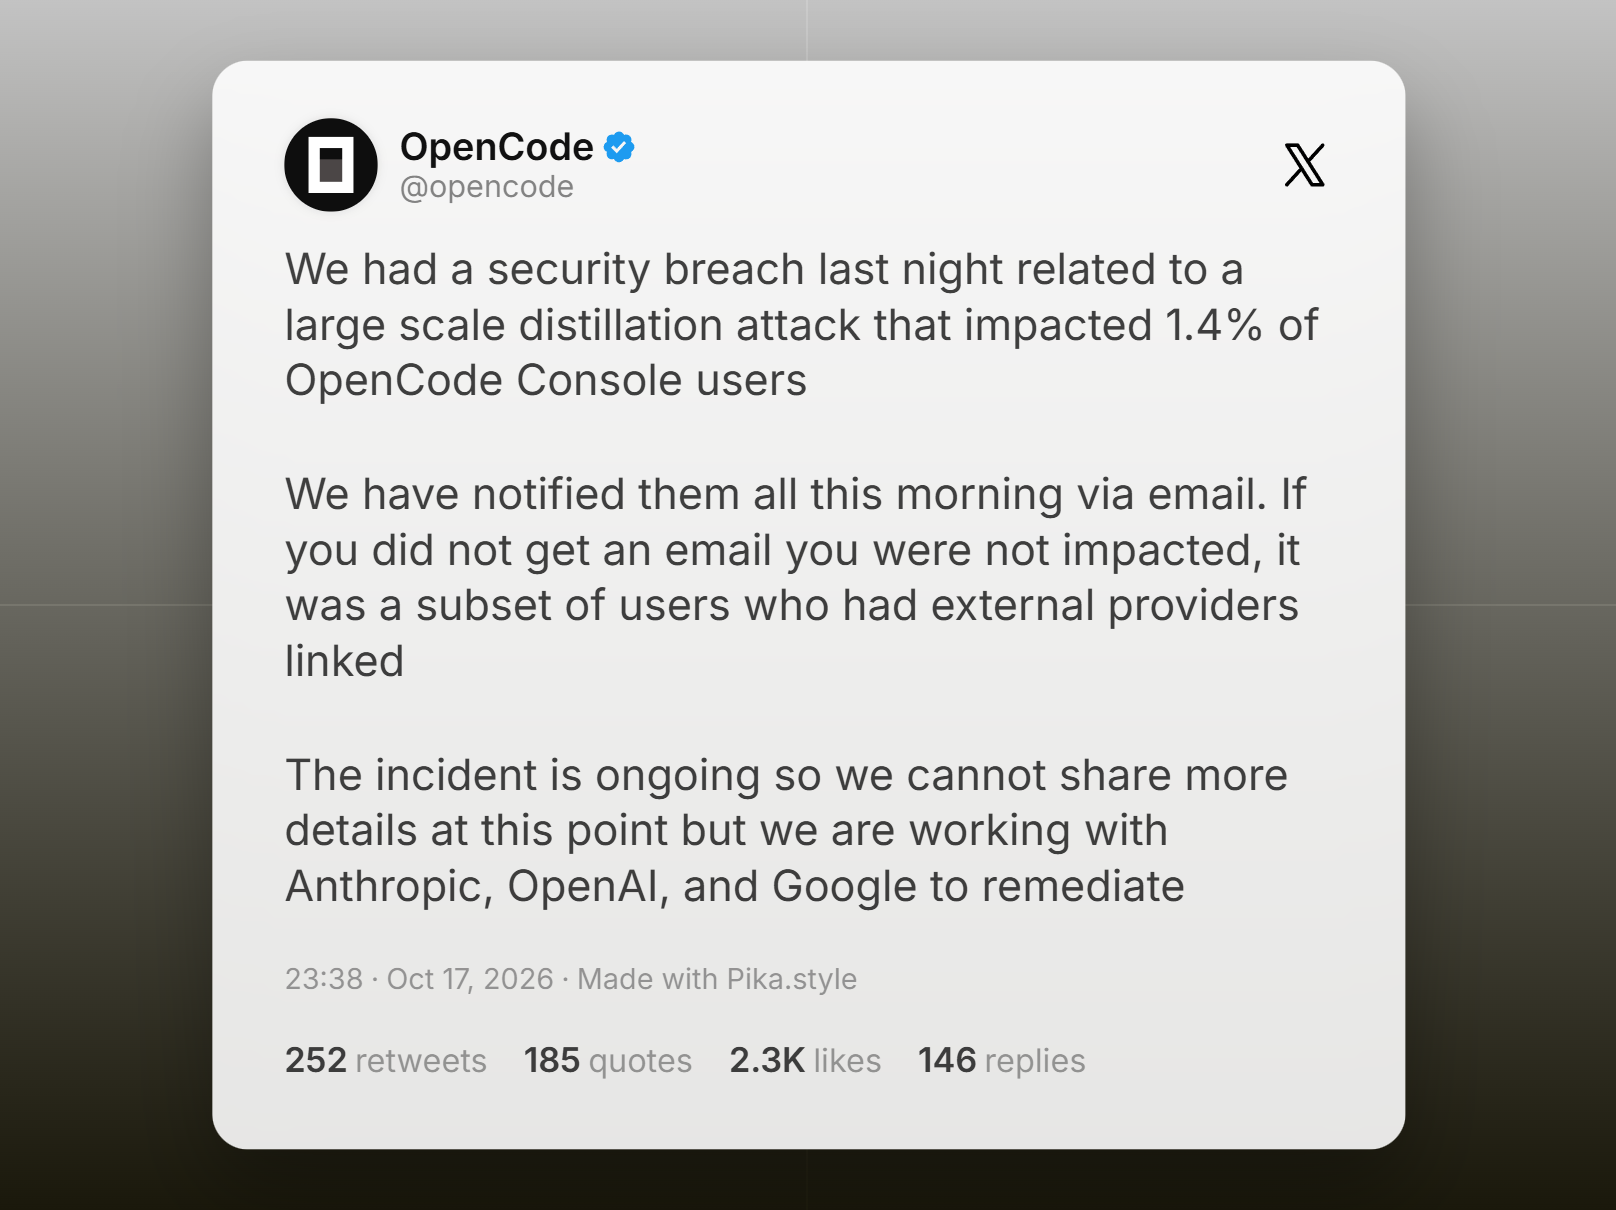
OpenCode has confirmed a security breach and says 1.4% of its Console users were affected. The company says the affected accounts were a subset of those with external providers linked. Everyone affected has been notified by email, and OpenCode says users who did not receive one were not impacted. The company linked the breach to a large-scale distillation attack, which involves collecting an AI model’s responses to train another model. OpenCode says the incident remains ongoing and that it is working with Anthropic, OpenAI and Google to address it. Affected users have been asked to revoke and replace their provider keys, update applications using them and review recent usage for unexpected activity.
Source(s)
 Add as a preferred source on Google


